



A computerized system validation (CSV) project can take anywhere from a few weeks to several months. The useful answer is not a single duration, because validation effort should follow the system’s intended use and risk. A stand-alone instrument with limited regulated data may move through validation relatively quickly. An LC-MS data system, automated liquid handling workstation, or bioreactor control platform that creates, changes, reviews, or stores GMP-relevant data usually needs a longer and more coordinated program.
For most teams, the practical question is not simply “How long does computerized system validation usually take?” It is: what must be ready before the system can be used with confidence in a regulated workflow? The schedule is shaped less by the number of test cases than by the clarity of requirements, supplier documentation, configuration decisions, interfaces, user roles, and evidence needed to demonstrate data integrity.
A realistic CSV plan begins by defining the system boundary. That sounds administrative, but it prevents one of the most common causes of delay: validating the instrument while overlooking the software, connected database, network storage, reporting tool, or interface that actually handles the data.
Typical CSV timelines by system scope
The ranges below are planning guides, not promises. They assume that the equipment is available, the intended process is reasonably defined, and the responsible quality, laboratory, engineering, and IT stakeholders can review documents without long gaps.
A bioreactor controller may appear straightforward when assessed only as a piece of equipment. The scope grows when its control software manages recipes, records pH and dissolved oxygen trends, communicates with plant systems, or supports batch decisions. The same applies to downstream centrifugation and separation systems when process parameters, alarms, and electronic batch evidence become part of the controlled record.
By contrast, a laboratory instrument that produces exploratory, non-decision-making data may require a lighter approach. “Lighter” does not mean undocumented. It means the validation activities should be proportionate to what could go wrong and the consequences if it does.
Why validation schedules expand
CSV is often delayed before testing even begins. The usual problem is not a lack of test scripts; it is that the team has not agreed on what the system is supposed to do, who owns each activity, or what records must be protected.
Requirements are incomplete or too generic
A user requirements specification should describe the intended use in operational terms. “The system must be compliant” is not testable. “Only authorized analysts may approve an analytical sequence, and the system must retain an attributable audit trail for changes to processing parameters” is testable.
Requirements also need boundaries. Does the scope include only acquisition software, or also processing, reporting, raw-data storage, backup restoration, and archive retrieval? A late decision to include those elements can reset risk assessment and testing work.
The supplier package does not match the actual configuration
Vendor documentation can reduce duplicated effort, particularly for standard software functions and installation activities. It cannot automatically validate the way a laboratory or manufacturing site has configured and uses the system. Teams still need to assess supplier evidence, identify gaps, and verify the functions that matter in their own process.
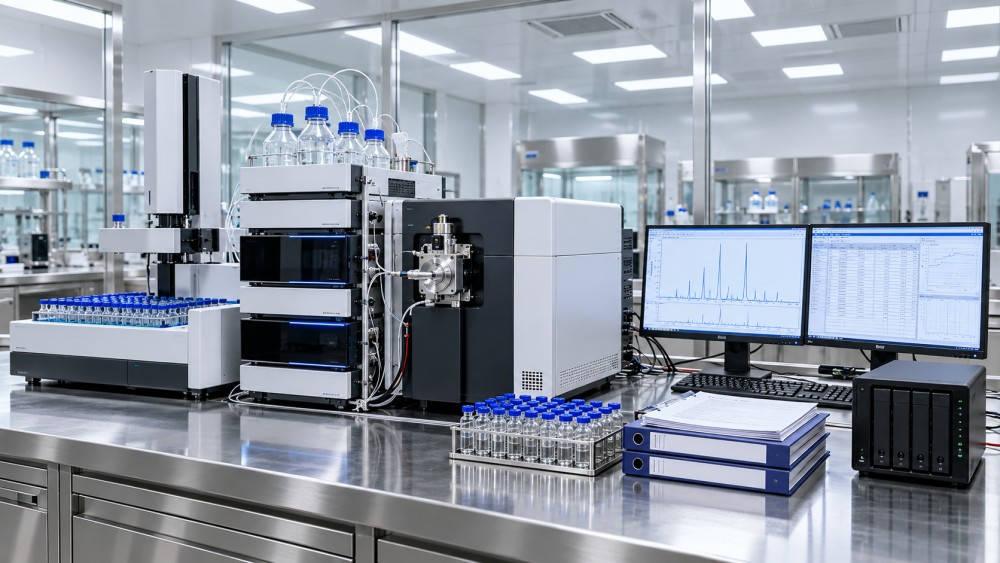
This distinction matters for LC-MS systems. A supplier may document the core software installation, but the site remains responsible for its user roles, approved processing methods, integration rules, report templates, review workflow, and retention arrangements. Validation takes longer when these site-specific choices are made after execution starts.
Interfaces create more work than the instrument itself
Interfaces are a major schedule variable because they introduce data transfer, ownership, reconciliation, error handling, and recovery questions. A liquid handler that exchanges sample identifiers with a laboratory information system is not only a pipetting platform. The validation scope must show that the correct sample information is transferred, failures are visible, data cannot silently disappear, and the workflow can be recovered in a controlled way.
It is risky to validate each connected application separately and assume the complete workflow is covered. The points where data move between systems deserve explicit challenge testing.
Data integrity controls are identified late
Electronic records require more than a password prompt. The team may need to assess unique user access, privilege levels, audit trails, time synchronization, electronic approvals, record retention, backup, restoration, and the ability to retrieve readable records later. These controls are easier to build into the design and configuration than to add after a nearly complete validation package has been reviewed.
In an analytical environment, a common weak point is focusing on whether results can be generated while neglecting whether method changes, reprocessing events, deleted injections, and review decisions can be traced and understood. The system can perform technically well yet still create a difficult inspection position if its records cannot explain how a final result was reached.
A practical way to estimate the project before committing to a date
Rather than asking a supplier for one universal CSV duration, work through five questions. The answers create a more defensible schedule and expose missing decisions early.
- What regulated decision does this system support? Consider release testing, batch production, stability work, quality control, development, or exploratory research. The impact of an incorrect, missing, or altered record determines the depth of scrutiny.
- What data enter, change, or leave the system? Map raw data, metadata, calculated results, reports, approvals, alarms, and exported files. Include manual transfers, spreadsheets, shared folders, and interfaces.
- How much is standard versus configured? Standard use of a mature platform may rely more heavily on assessed supplier documentation. Custom scripts, bespoke reports, integrations, and complex workflow rules increase site testing and review time.
- What must be available at go-live? Approved procedures, trained users, support ownership, access administration, backup and recovery arrangements, incident handling, and change control are operational readiness items, not afterthoughts.
- Who can make decisions promptly? A project may have enough technical staff but still stall when quality reviewers, IT security, instrument vendors, or process owners are unavailable to approve requirements, deviations, and release decisions.
These questions also help distinguish validation work from equipment qualification. Installation qualification, operational checks, performance activities, calibration, and method validation may overlap with CSV but do not automatically replace it. The relationship depends on the system and process. A good plan coordinates them so the same activity does not need to be repeated, while still preserving clear evidence for each objective.
Where teams lose time unnecessarily
One avoidable mistake is treating CSV as a documentation project that starts after the system is configured. If the validation team joins only at the end, it may discover that account roles are too broad, audit trails are not enabled, system time is unmanaged, or a workflow cannot be reproduced from retained records. Correcting configuration late can be more disruptive than the original implementation.
Another mistake is writing exhaustive test scripts for every theoretical software feature. A risk-based approach does not mean testing less without reason; it means concentrating evidence on intended use, critical functions, credible failure modes, and controls that protect data and product decisions. Testing a function that nobody will use rarely strengthens the validation case. Failing to test a configuration that governs data approval clearly does not help.
Teams also underestimate review cycles. A test may execute in a day but take much longer to resolve when there is a deviation, unclear expected result, incomplete attachment, or disagreement about whether a failure affects release. Building time for document review, defect triage, retesting, and quality approval produces a more realistic schedule than counting execution days alone.
How to shorten CSV without reducing control
The most effective schedule improvement is preparation before installation. Create the intended-use statement, preliminary system inventory, risk assessment, and responsibility map while procurement and site readiness are still underway. Request supplier documentation early and assess it against the planned configuration rather than waiting for commissioning to finish.
Use a simple traceability structure from requirements to risk controls and test evidence. This prevents the late-stage search for proof that each important requirement was addressed. Keep configuration decisions controlled, especially user roles, audit-trail settings, report templates, calculation logic, and interface mappings. Frequent unrecorded changes during testing create rework because prior results may no longer represent the production configuration.
For specialized laboratory and bioprocessing equipment, technical intelligence can be useful when the team needs to understand where the regulated boundary sits. BLES focuses on the systems where this question commonly becomes complex: automated liquid handling, analytical platforms, bioreactor controls, and downstream processing equipment. The useful objective is not a generic validation checklist, but a clear connection between process behavior, electronic records, and GMP-ready evidence.
When a short validation timeline is a warning sign
A short timeline can be appropriate for a limited, low-risk, well-documented system with few configuration changes. It becomes a warning sign when the system controls a GMP-relevant process, manages critical analytical data, contains custom functions, or connects to several applications, yet the plan includes only an installation check and a few basic tests.
Ask whether the schedule explicitly includes requirements, risk assessment, supplier assessment, installation and configuration evidence, functional testing, deviation management, procedures, training, final review, and formal release. If these activities are missing from the estimate, they have not disappeared; they have usually been deferred to a point when the project is under more pressure.
Frequently asked questions
Can a vendor validate the system for us?
A vendor can provide valuable qualification documents, configuration support, and technical evidence. The regulated organization still needs to determine whether the system, as implemented for its intended use, is fit for purpose and adequately controlled within its own quality system.
Does every laboratory instrument need the same level of CSV?
No. The level of validation should reflect risk and intended use. A system supporting quality decisions or regulated records generally needs more evidence than an isolated tool used only for early exploratory work.
Does upgrading software require full revalidation?
Not automatically. The right response depends on what changed and what functions, interfaces, records, or controls could be affected. A documented impact assessment should define targeted regression testing and any updates required to controlled records.
When is the system ready for routine use?
Routine use should begin after the agreed validation evidence is reviewed and approved, open issues are handled through an appropriate process, users are trained, and operational controls such as access management, support, and backup arrangements are in place.
The fastest credible CSV program is not the one with the fewest documents. It is the one that establishes scope early, applies effort where failure would matter, controls configuration changes, and reaches go-live with evidence that the people operating the system can trust its records.
Related News
- How to assess audit trails in analytical data integrity solutionsOct 16, 2026Dr. Elara Sterling
- How user licensing affects laboratory validation system pricingOct 14, 2026Dr. Elara Sterling
- How secure data integrity systems support GMP audit readinessOct 12, 2026Dr. Elara Sterling
- How laboratory validation systems support GMP data integrityOct 10, 2026Dr. Elara Sterling
Related News
- 00
0000-00
How to assess audit trails in analytical data integrity solutions - 00
0000-00
How to assess an automated liquid handling platform's throughput - 00
0000-00
How user licensing affects laboratory validation system pricing - 00
0000-00
When does pathogen sample processing require a Class III cabinet? - 00
0000-00
How secure data integrity systems support GMP audit readiness
Dr. Elara Sterling
Weekly Insights
Stay ahead with our curated technology reports delivered every Monday.